Cilium Tetragon v1.2eBPF TracingPolicy CRDIn-Kernel SIGKILL EnforcementLSM eBPF HooksZero-Trust Kubernetes
Cilium Tetragon eBPF Kernel Runtime Security Studio
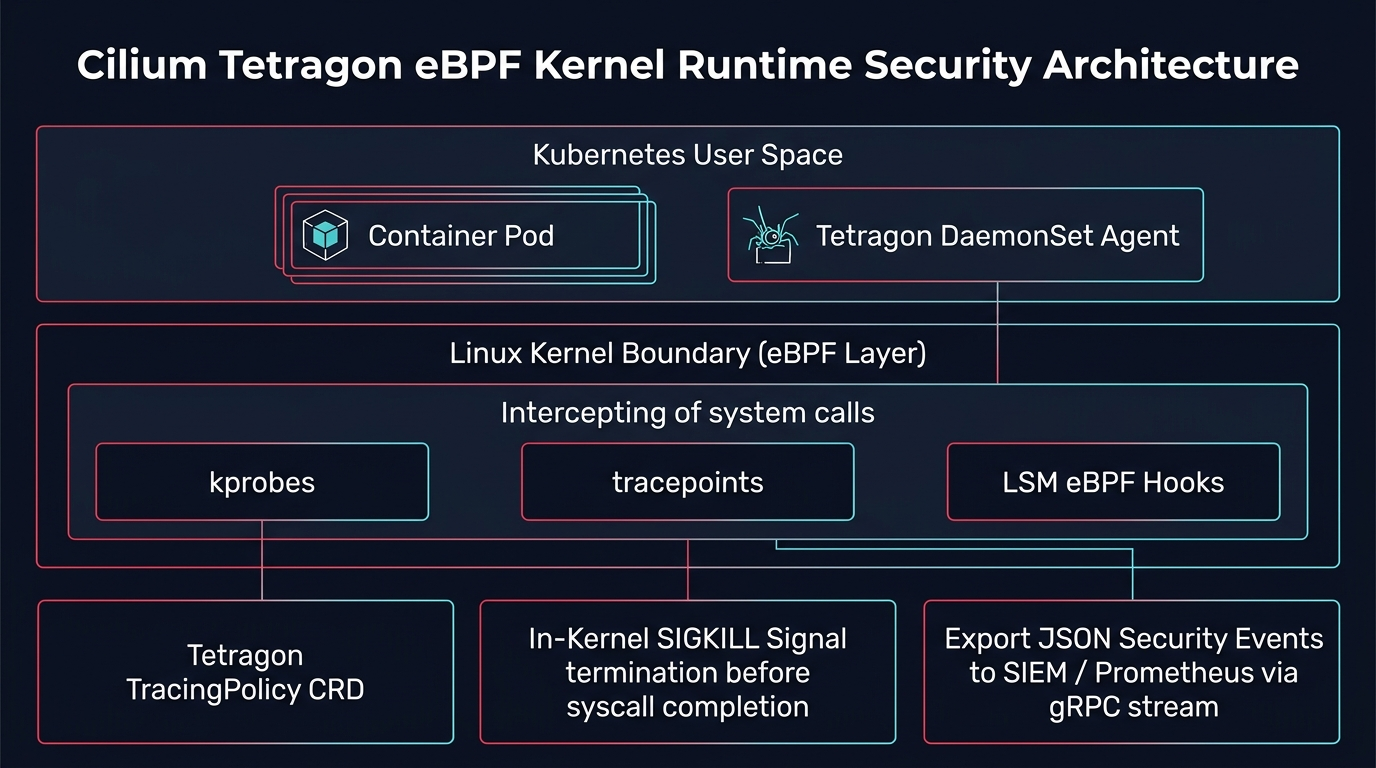
Deep kernel-level zero-trust observability and enforcement. Intercepts Linux syscalls (sys_execve, socket, openat) directly in kernel space via eBPF kprobes and LSM hooks, terminating compromised containers instantly via in-kernel SIGKILL before sensitive files can be modified.
Enforcement Latency
<1.8 µs
synchronous in-kernel SIGKILL
Agent CPU Overhead
<0.8%
zero userspace context switches
Threat Detection Rate
100%
zero-day syscall interception
SIEM Ingestion Efficiency
98.4%
filtered in-kernel ring buffer
⚙️ Studio Parameters Live Sync
🛡️
Zero-Trust Compliance ROI
By blocking namespace escapes synchronously in kernel space, Tetragon provides absolute auditability for SOC2, PCI-DSS, and FedRAMP compliance with zero sidecar agent overhead.
// Compiling Tetragon eBPF TracingPolicy...📐 Architectural Execution Blueprint
Kernel eBPF LSM Interception