🔍
🛡️
No Matching Security Studios Found
Try adjusting your filters or refining your search keywords.
Live Workspace
⚡ WASM Simulated
DevSecOps Visual Flow Canvas
Open the dedicated 6-stage supply chain security graph: signed commits, Semgrep AST scans, Syft SBOM generation, Trivy CVE gates, Cosign keyless signatures, and Kyverno admission webhooks.
Launch DevSecOps Flow →🤖 Provision New DevSecOps Repos
Automatically create the 5 proposed next-generation DevSecOps repositories using the GitHub CLI:
# Run in terminal:
node scratch/provision-devsecops-repos.js
🛡️ DevSecOps Architecture Flow
End-to-end cryptographic provenance, vulnerability gating, and in-kernel runtime security topology:
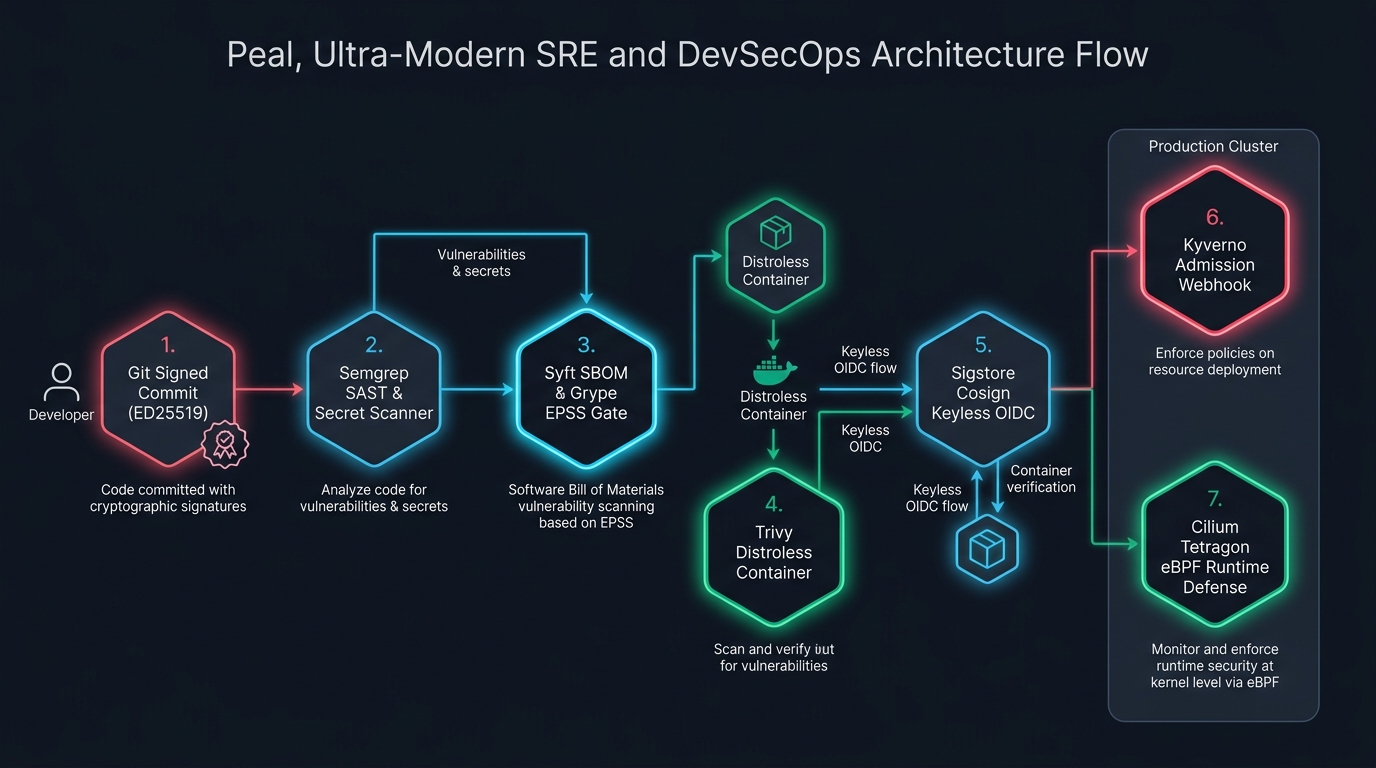
📊 SLSA Attestation Sequence
graph TD
G[1. Git Sign ED25519] --> S[2. Semgrep SAST Gate]
S --> B[3. Syft SBOM & Grype]
B --> C[4. Cosign Keyless Sign]
C --> K[5. Kyverno Admission Webhook]
K --> T[6. Tetragon Kernel Monitor]
⚡ SRE Quick Verification
Verify container image signature against Rekor transparency log:
cosign verify --certificate-identity-regexp '.*@github\.com' ghcr.io/pradeep/service:sha-latest